Secure Software Design
A Feature Flag Is Not an Authorisation Check
Separate feature rollout from access control so a hidden interface cannot become the only protection around a sensitive server action.

Technology that earns its place.
Separate feature rollout from access control so a hidden interface cannot become the only protection around a sensitive server action.
A webhook’s JSON can look correct and still be untrusted. Keep the original body, verify the signature and test failure before processing the event.
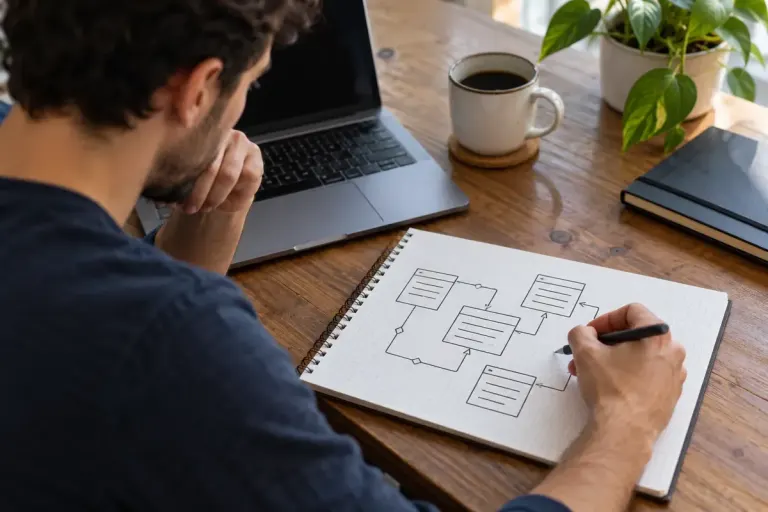
Define how deletion affects related records, user expectations and recovery before implementing the button or choosing a database cascade rule.
Decide which responses may be shared, preserve authorisation checks and test caches with separate users before enabling them for account pages.
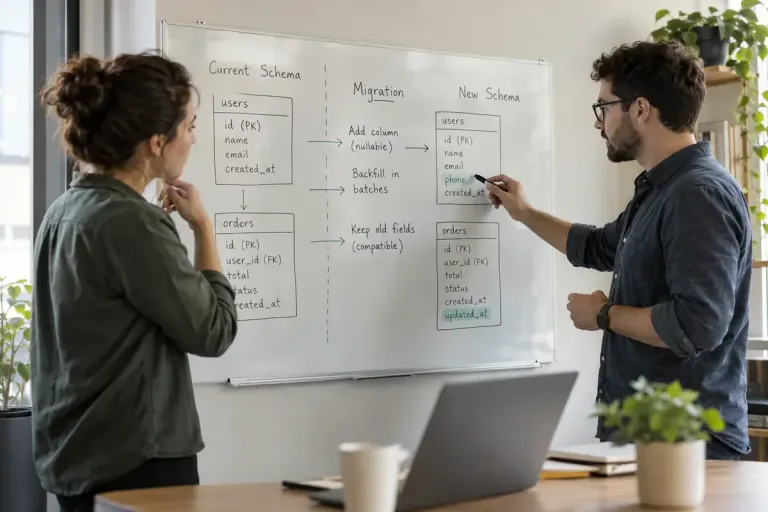
Plan a database change around overlapping application versions, separating schema expansion, data backfill and removal of obsolete fields.
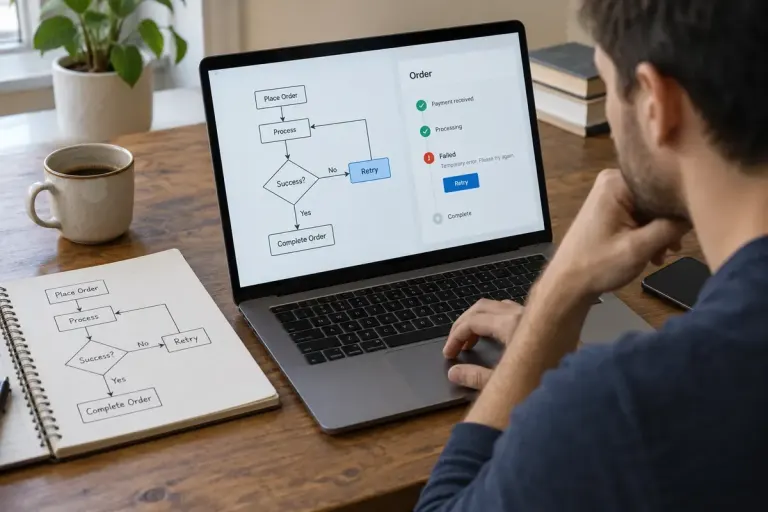
Design retries around one intended operation so a timeout does not become a second order, with clear keys, state checks and provider-specific rules.
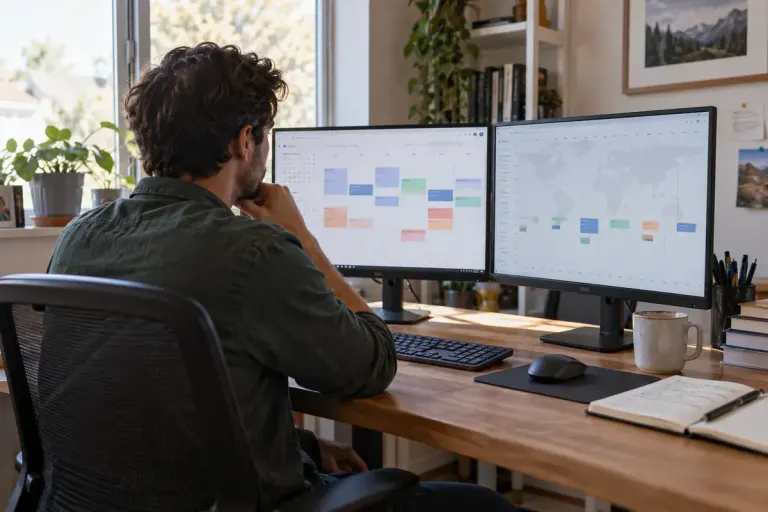
Prevent scheduled-email mistakes by making the intended time zone, daylight-saving behaviour and test result explicit before sending.
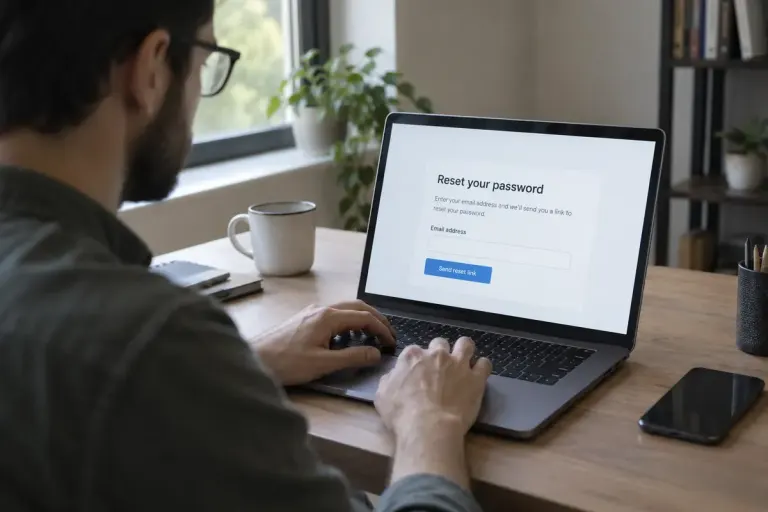
Design password-reset responses that help legitimate users without confirming account membership, and support the interface with secure server behaviour.
Make upload requirements visible before submission and provide an error that tells customers how to recover without losing the rest of their work.